
Engineered for trust.Built for filing season.
Secure, serverless architecture protects sensitive filing data and scales automatically when volume peaks.
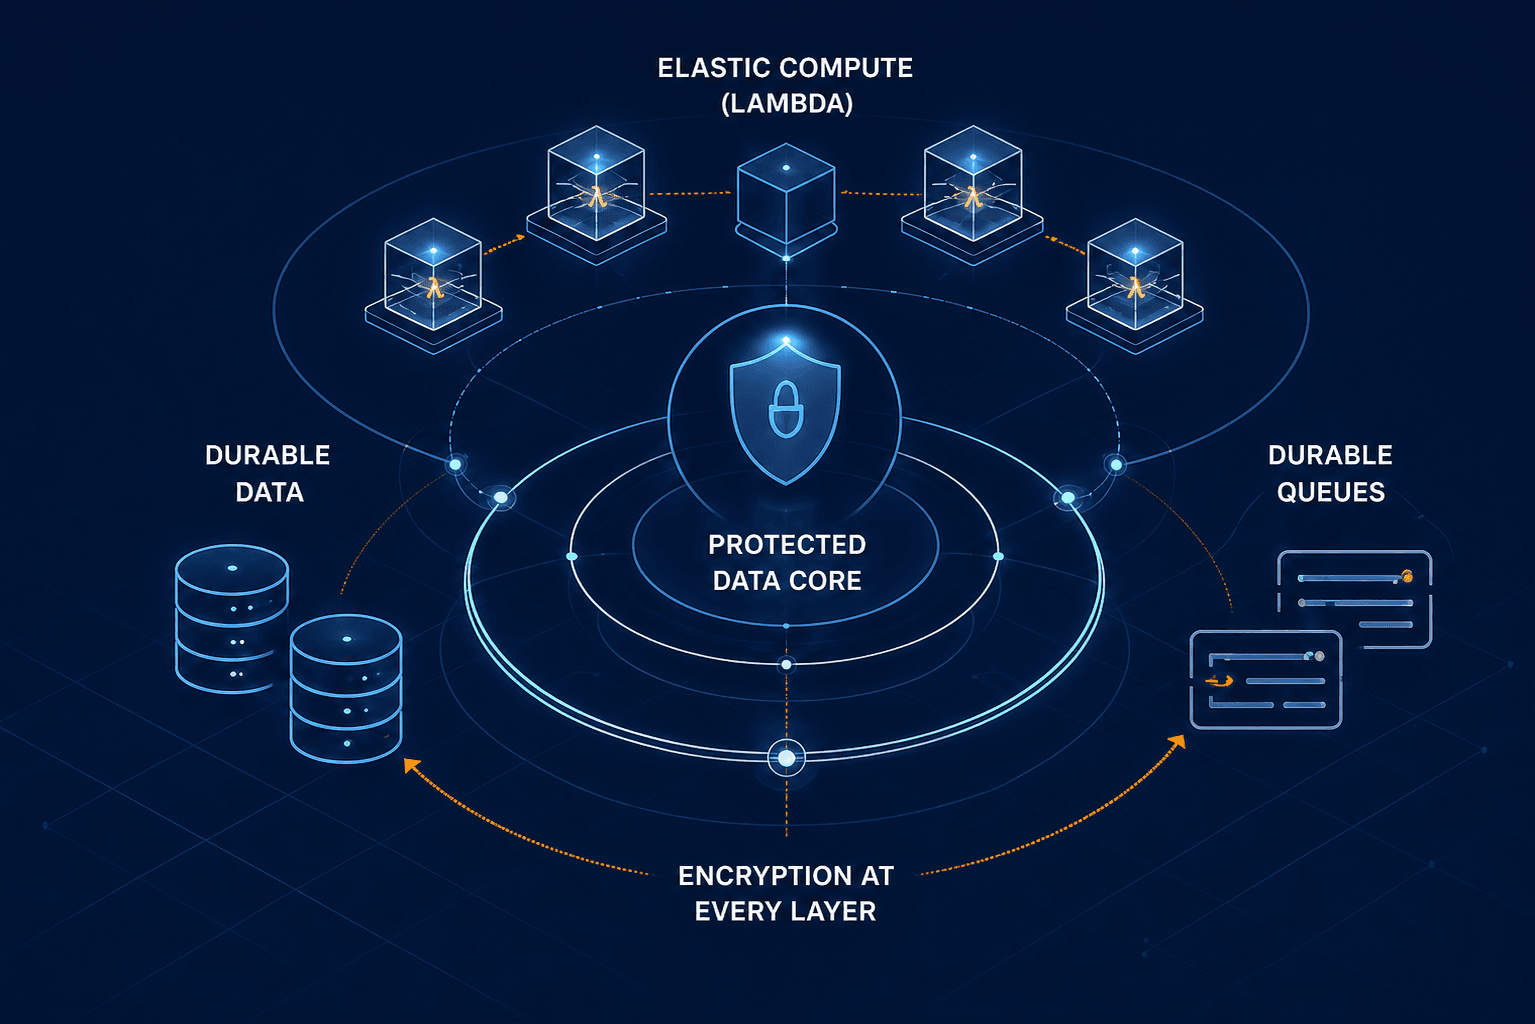
- SOC 2 Controls
- Encryption at Every Layer
- Tenant Isolation
- Resilient by Design
Controls backed by independent review
SOC (Service Organization Controls) reports examine the controls service organizations use to protect customer data. Our SOC 2 report is audited by a qualified independent CPA firm against the AICPA Trust Services Criteria.
- Security
- Availability
- Processing Integrity
- Confidentiality
- Privacy
A modern stack built for high-stakes data
Protected Edge
Rust on AWS Lambda
Amazon DynamoDB
Durable SQS Workflows
AWS KMS Encryption
Reliable
Built to handle peak season with consistent performance.
Durable
Durable storage supports reliable access and recovery.
Scalable
Serverless architecture scales automatically with demand.
Secure
Defense in depth protects sensitive filing data.
Security in depth
1. Edge protection
- TLS 1.2+ in transit
- WAF and rate limiting
- DDoS mitigation
2. Identity & access
- MFA and passkeys
- Least privilege access
- Tenant isolation
3. Memory-safe application
- Rust-based services
- Input validation
- Secure by default
4. Application-layer encryption
- Authenticated encryption
- Keyed search tokens
- KMS-managed keys
5. Audited operations
- Immutable audit trails
- Change monitoring
- Comprehensive logging
Designed to finish the work
Every filing moves through a resilient workflow built for recovery.
Atomic write
Committed once or not at all.
Durable queue
Work persisted for reliability.
Idempotent worker
Processes safely without duplicates.
Verified completion
Outcome confirmed and recorded.
- Retry with backoff
- Reconciliation
- Dead-letter handling
Security you can trust. Performance you can rely on.
Get started with a platform built for sensitive, high-volume filing. Read our security design article.